Essential Cyber Recovery Capabilities That Matter
Essential cyber recovery capabilities keep mission systems operating after an attack, with fast containment, trusted restoration, and defensible evidence.
Identity Threats Put Mission Continuity at Risk
Identity threats turn trusted access into a breach path. See how continuous verification, rapid containment, and recovery protect critical operations.
When Should Companies Invoke Containment?
Know when companies should invoke containment to stop active threats, preserve evidence, protect operations, and restore control before damage spreads.
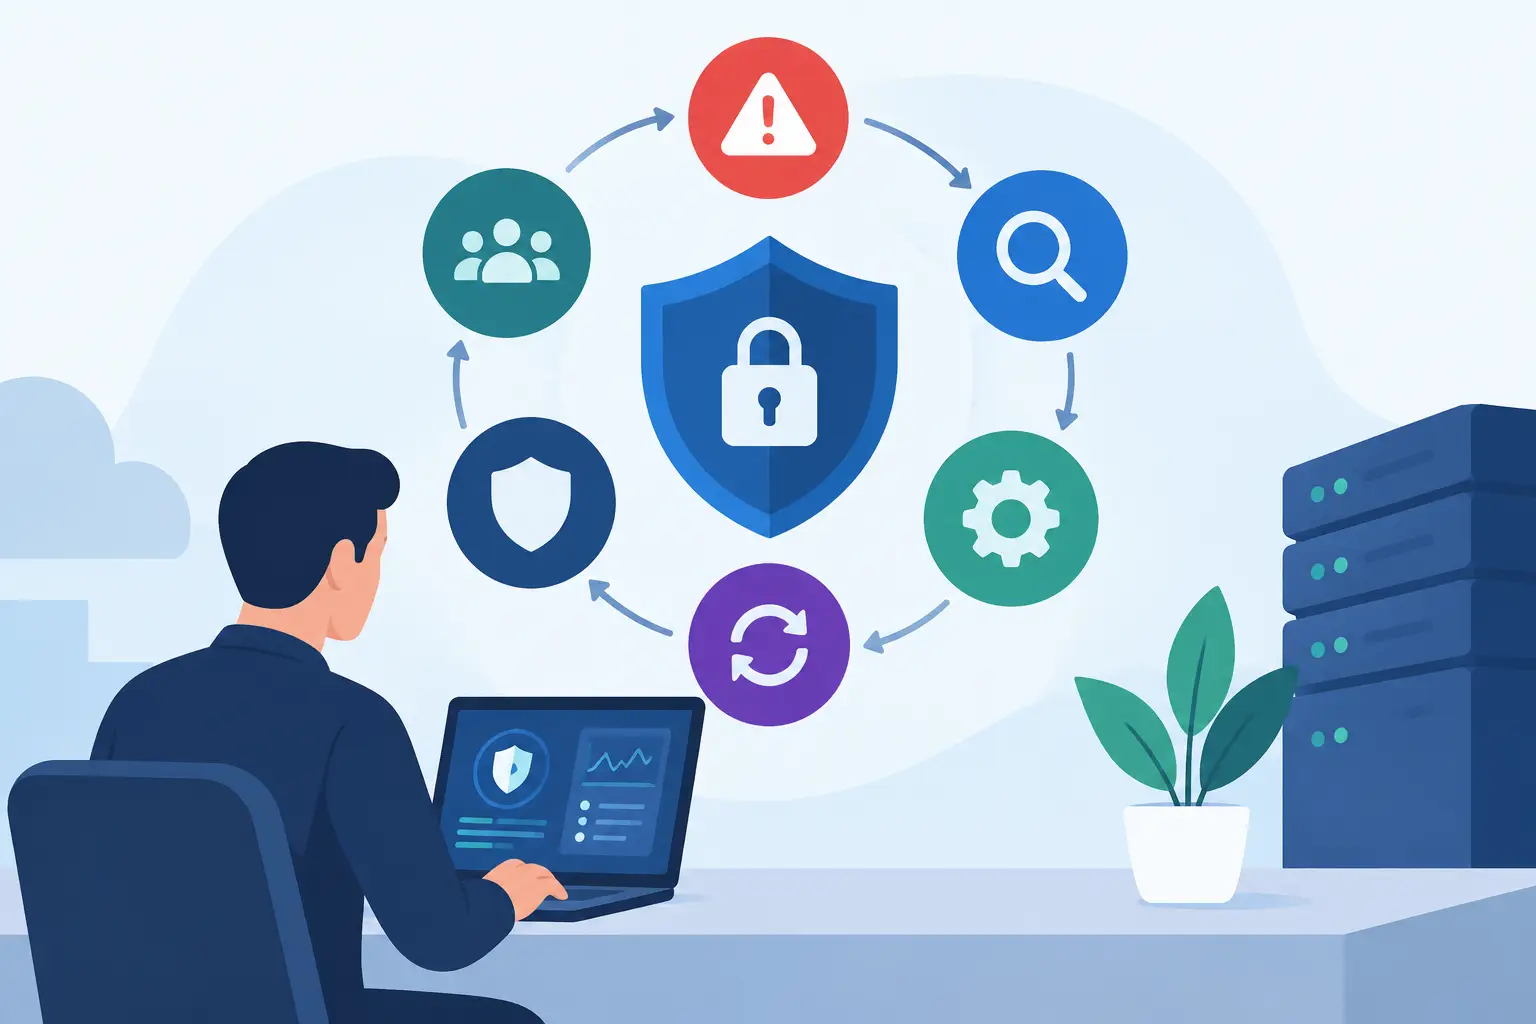
What Incident Response Platforms Must Do
Incident response platforms must detect, contain, investigate, and recover across the enterprise. See what separates operational defense from alert noise.
Enterprise Breach Recovery Checklist for Leaders
Use this enterprise breach recovery checklist to contain threats, restore operations, preserve evidence, and protect the mission after an active attack.
How to Secure OT Assets Without Stopping Production
Secure OT assets with Zero Trust controls that verify every connection, limit blast radius, and keep production moving through cyber incidents safely.
Critical Infrastructure Defense Guide for Leaders
This critical infrastructure defense guide shows leaders how to reduce cyber risk, contain attacks fast, and keep essential operations moving at scale.
How to Configure Phishing Resistant Authentication
Learn how to configure phishing resistant authentication with FIDO2, conditional access, recovery controls, and continuous Zero Trust verification daily.
FedRAMP vs CMMC Compliance for Federal Work
FedRAMP vs CMMC compliance affects different federal missions. See who must comply, how controls differ, and how to build evidence that stands up in audits.
Security Incident Containment Guide for Leaders
This security incident containment guide helps enterprise leaders isolate threats, protect operations, preserve evidence, and restore control quickly.
CMMC Continuous Monitoring Guide for Defense Teams
A CMMC continuous monitoring guide for defense contractors that turns control evidence, threat detection, and response into daily operational discipline.
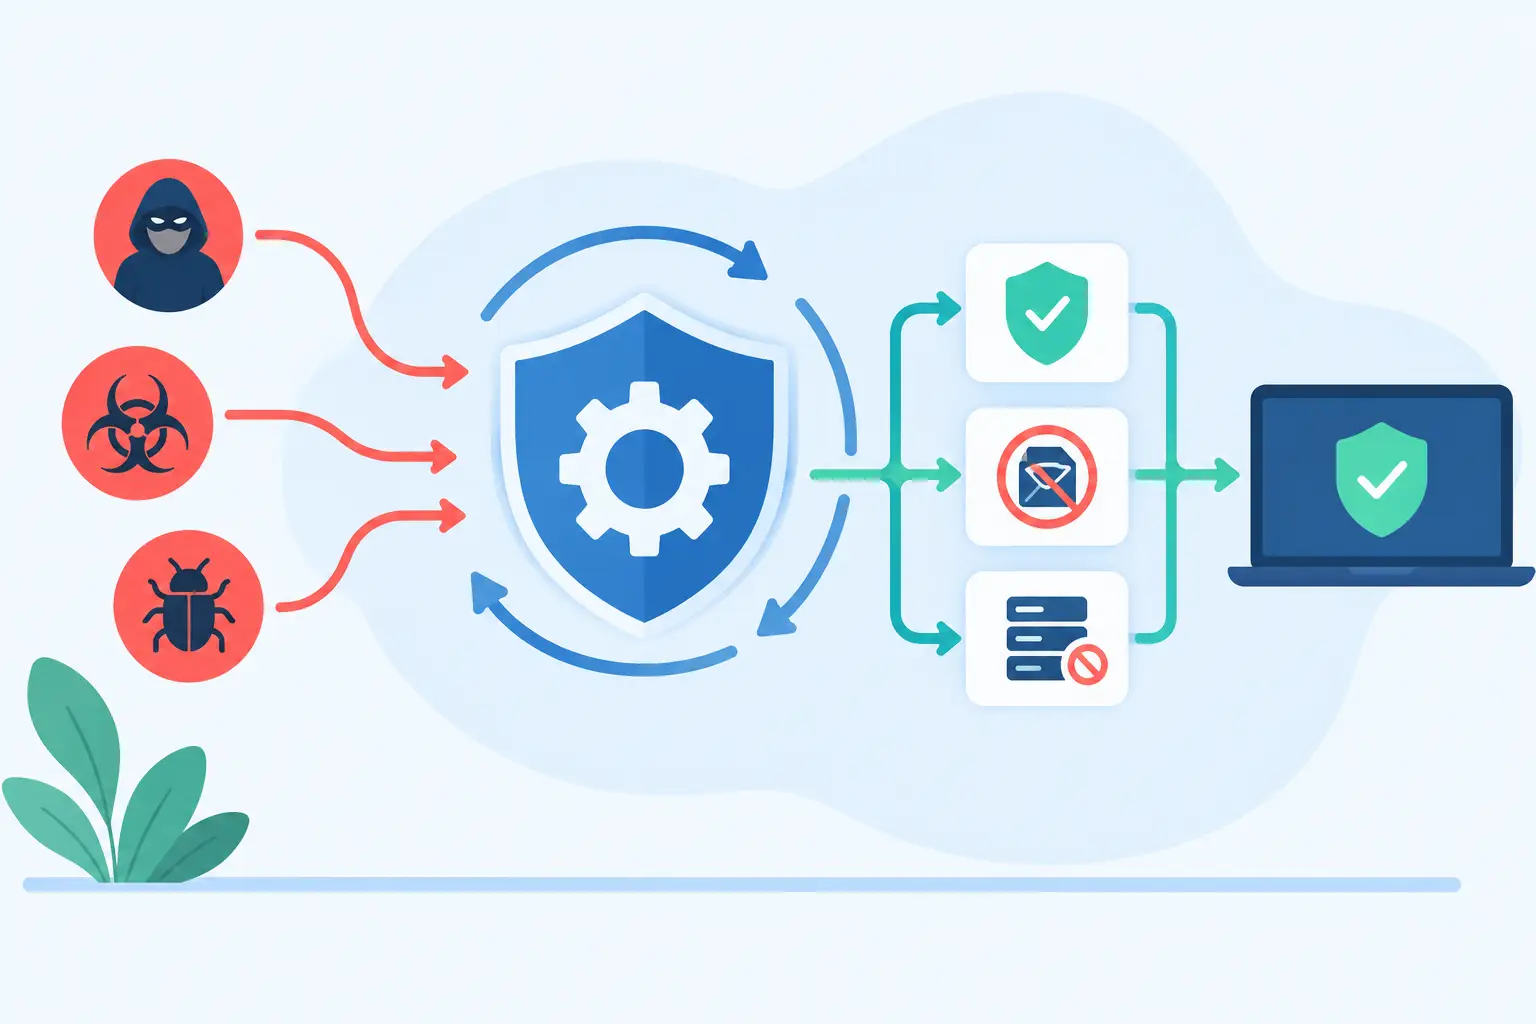
How to Automate Threat Containment Workflows
Automate threat containment workflows with verified signals, Zero Trust controls, and signed response evidence that keeps critical operations moving every day.
Federal Zero Trust Compliance Guide for Leaders
This federal zero trust compliance guide gives agency and contractor leaders a practical path to evidence, containment, and mission-ready controls daily.
How to Choose the Best Cyber Incident Response Firms
Evaluate the best cyber incident response firms by speed, forensic depth, recovery discipline, and containment that keeps operations moving under attack.
PQC Adoption Requires a Migration Plan Now
PQC adoption is a security decision, not a crypto upgrade. Inventory cryptography, prioritize migration, protect access, and preserve mission continuity.
What Causes Account Takeover in the Enterprise?
Learn what causes account takeover, how attackers exploit identity gaps, and how Zero Trust limits impact before operations are disrupted enterprise-wide.
Top Zero Trust Security Tools for Enterprise Defense
Compare top zero trust security tools for identity, endpoints, data, and operations. See how teams contain threats fast and preserve operations daily.
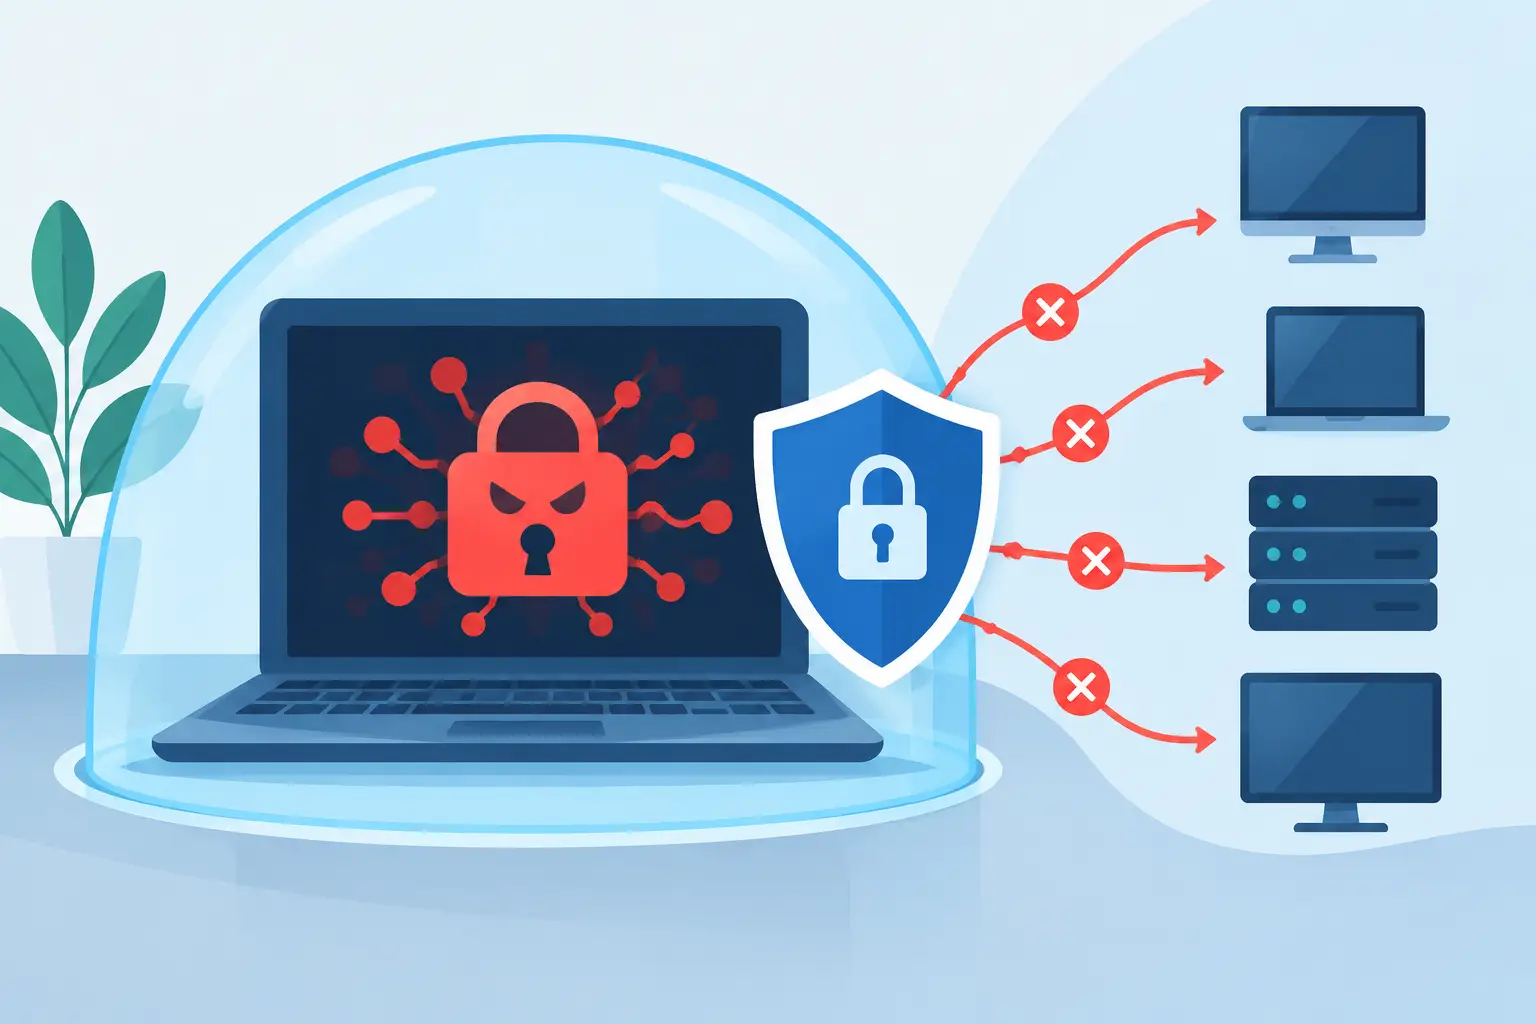
How to Contain Ransomware Before It Spreads
Learn how to contain ransomware using rapid isolation, identity controls, evidence preservation, and recovery actions that protect critical operations.
MDR Versus SOC Services: What Defends Faster?
MDR versus SOC services: compare speed, coverage, control, and incident response to choose the right cyber defense model for your enterprise today.
Ransomware Response Services That Hold the Line
Ransomware response services contain attacks fast, preserve evidence, and restore critical operations with command, control, and speed. When it counts.
Digital Asset Protection Guide for Enterprise Defense
This digital asset protection guide shows leaders how to identify mission assets, enforce Zero Trust, contain threats, and recover operations quickly.
Enterprise Cybersecurity Strategy That Holds
Build an enterprise cybersecurity strategy that verifies every request, contains threats fast, and preserves the evidence and operations leaders need.
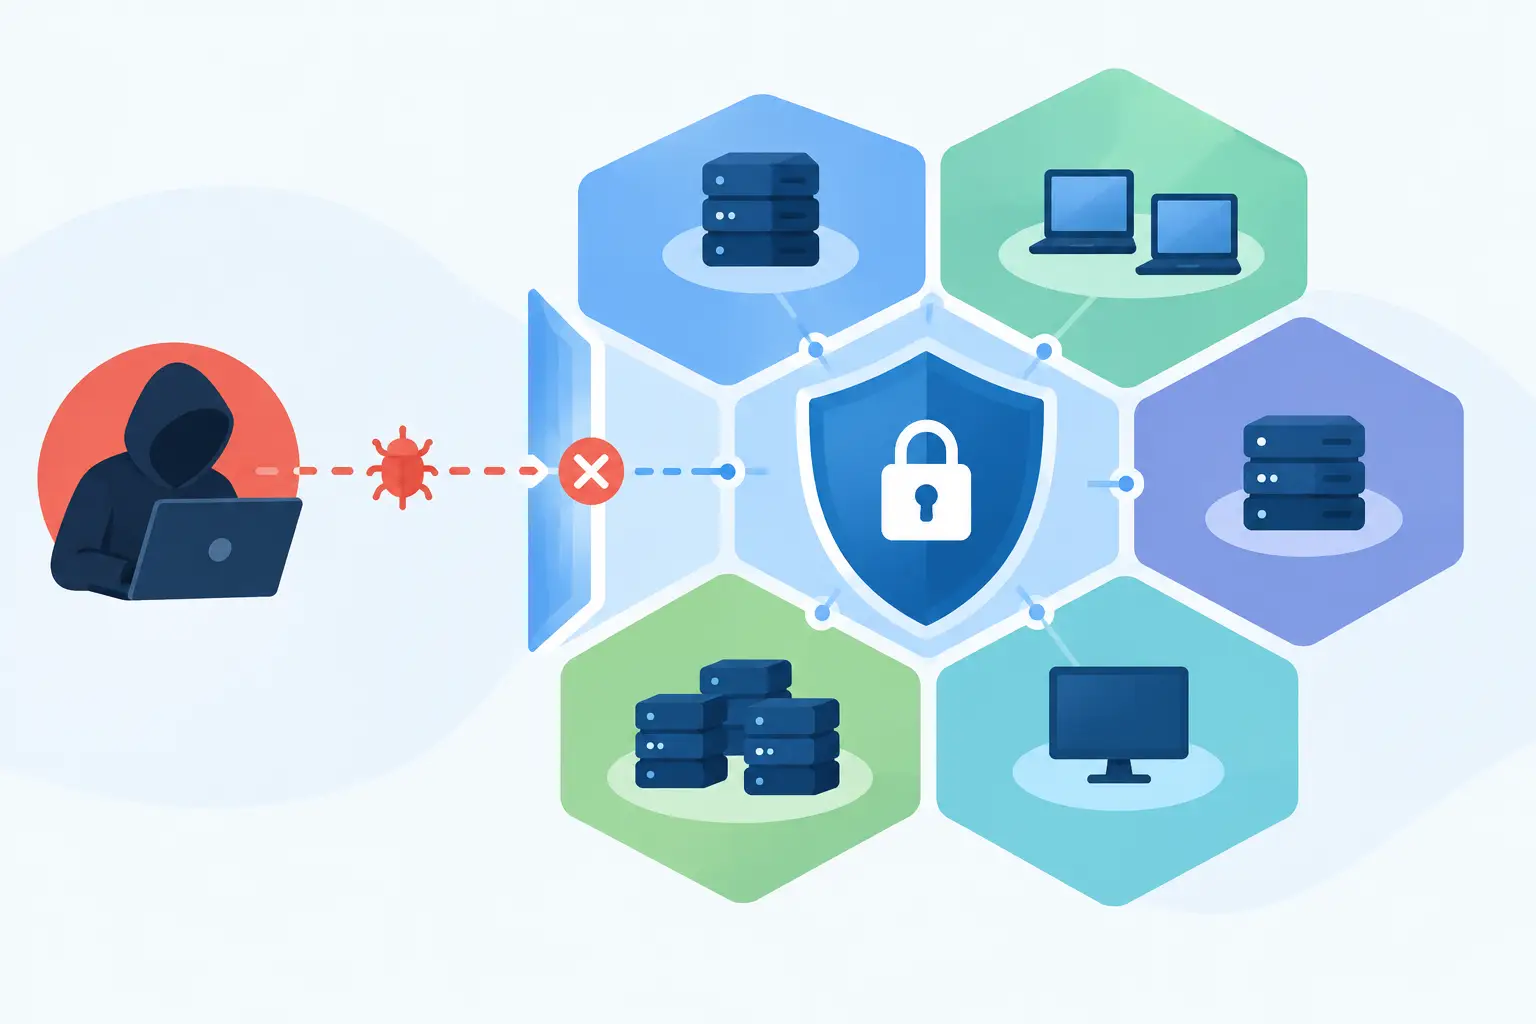
Microsegmentation Limits Breaches Before They Spread
Microsegmentation contains threats by enforcing least-privilege access between workloads, users, and systems, protecting operations when a perimeter fails.
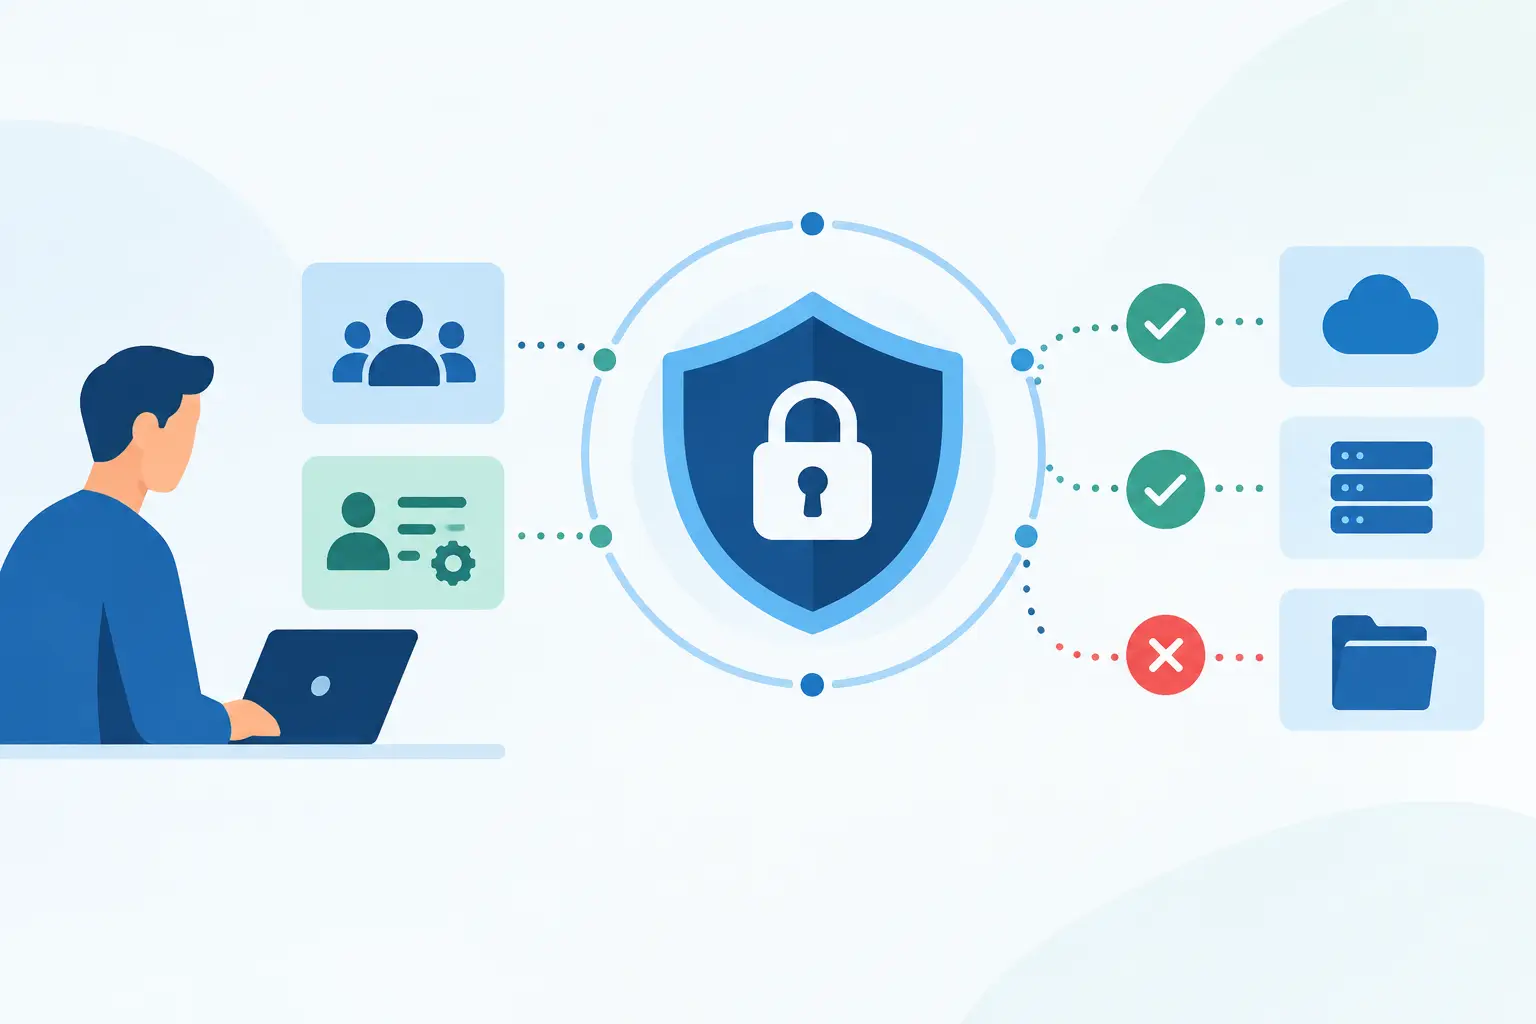
ABAC / RBAC Permissions for Zero Trust Security
ABAC / RBAC permissions make Zero Trust enforceable, limiting access by role, context, and risk to contain compromise and protect mission systems today.
Account Takeover Recovery That Restores Control
Account takeover recovery demands more than a password reset. Contain the attacker, restore trusted access, preserve evidence, and protect operations fast.
How to Restore Breached Systems Without Reopening Risk
Learn how to restore breached systems with evidence-led containment, clean recovery, identity control, and validation that keeps operations moving securely.
Best Privileged Access Controls for Zero Trust
Assess the best privileged access controls for Zero Trust: JIT elevation, phishing-resistant MFA, session oversight, policy enforcement, and recovery at scale.
Business Continuity Cybersecurity Guide for Leaders
A business continuity cybersecurity guide for leaders: contain threats, restore operations, and preserve audit-ready evidence under pressure when it counts.

A System Access Restoration Example Under Fire
See a system access restoration example that shows how Zero Trust containment, verified recovery, and audit evidence return operations to control fast.

Threat Hunting Review for Active Threats
A threat hunting review reveals whether your security team can find, contain, and prove action against active threats before operations fail in time.

SIEM, UDFIR and SOAR: Contain Threats Faster
SIEM, UDFIR and SOAR unite detection, investigation, and response to contain cyber incidents faster while preserving evidence and continuity at scale.

Zero Trust & PQC: Security Built for What’s Next
Zero trust & PQC prepares enterprise access for cryptographic change while enforcing every request, containing threats, and preserving continuity at scale.

How to Recover Systems After a Cyber Attack
Learn how to recover systems after cyber attack with containment, forensic proof, staged restoration, and controls that keep the mission operating now.

Third Party Breach Response Planning That Holds
Third party breach response planning gives leaders a tested path to contain supplier incidents, protect operations, preserve evidence, and recover well.
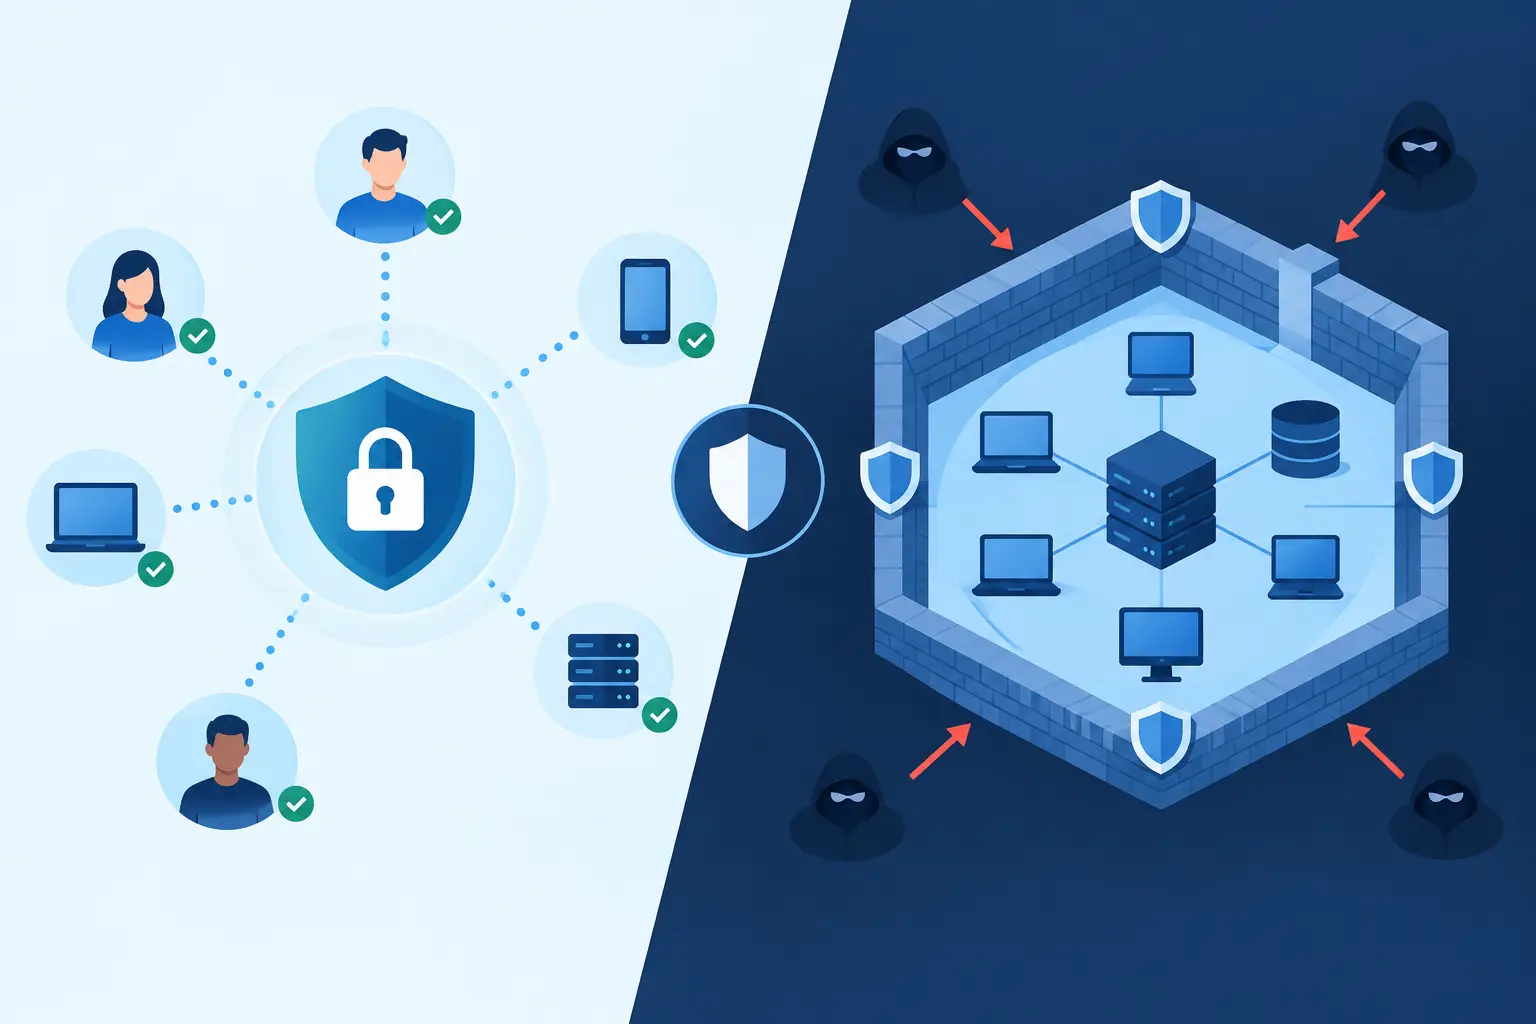
Zero Trust vs Perimeter Security: What Holds?
Zero trust vs perimeter security determines how far an intruder can move after first access. See which model protects mission-critical operations at scale.

Zero Trust and Mobility Without Exposure
Zero trust and mobility require continuous checks on identity, device posture, network context, and data access to contain threats before operations stop.
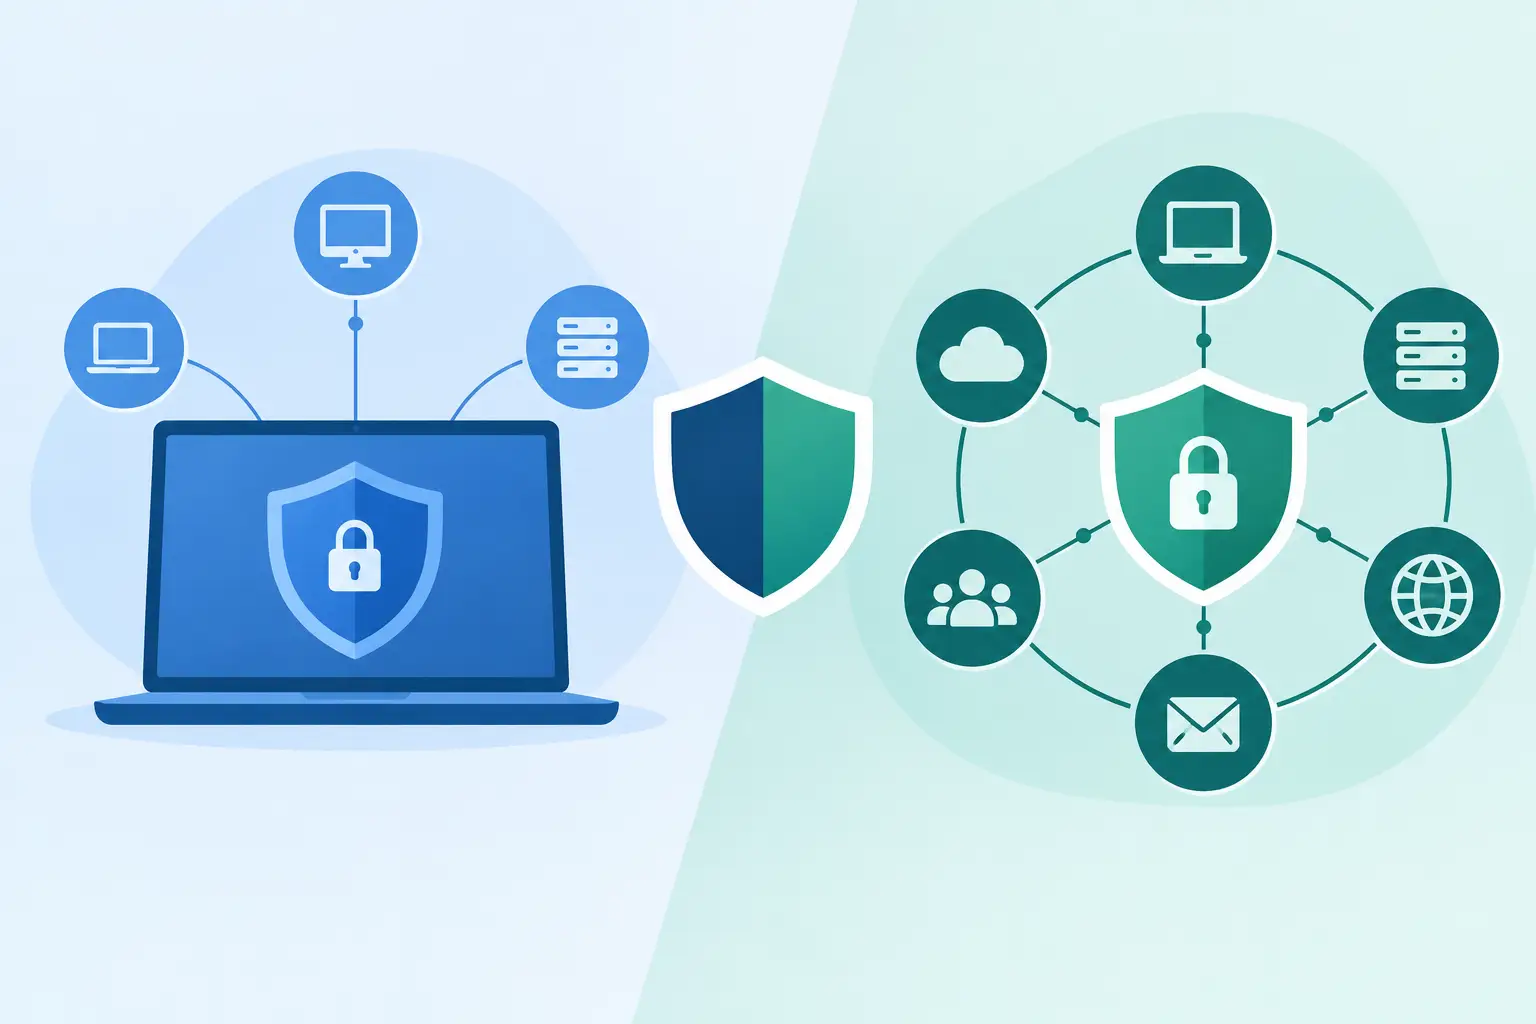
EDR vs XDR: Which Detection Model Holds?
EDR vs XDR shapes how quickly teams detect, contain, and document cyber incidents across endpoints, identity, network, and data when pressure is highest.

An Insider Threat Recovery Example in Action
An insider threat recovery example shows how decisive containment, verified restoration, and audit evidence protect operations after an internal misuse.

Ransomware Recovery Examples That Protect Operations
Ransomware recovery examples show how decisive containment, clean restoration, and auditable evidence keep critical operations moving after an attack.
What Is Cyber Resilience? A Business Continuity Test
What is cyber resilience? Learn how Zero Trust, rapid containment, recovery, and tested response plans keep critical operations moving after major attacks.
PQC vs Save Now Decrypt Later Risk Explained
PQC vs Save Now Decrypt Later is a present-tense risk. See how Zero Trust and cryptographic agility protect sensitive data before quantum attacks arrive.

7 Ways to Protect Sensitive Business Data
Learn how to protect sensitive business data with Zero Trust controls that contain threats, preserve evidence, and keep critical operations moving daily.

Post-Quantum Cryptography Is a Security Deadline
Post-quantum-cryptography is an operational security priority. Learn how to inventory exposure, set crypto agility, and protect the migration path now.

Governing What You Cannot See: AI Governance After the EU Deferral
The EU deferred its high-risk AI obligations to 2027. The requirements did not change, only the date, and the transparency duties are already in force.

Cybersecurity Tabletop Exercise for Executives
A cybersecurity tabletop exercise for executives tests authority, containment, communications, and recovery before a real incident strikes the enterprise.

Security Architecture Assessment Services That Hold
Security architecture assessment services expose the gaps between policy and enforcement, helping leaders contain threats and keep operations moving safely.

Why Insider Threats Go Unnoticed in Enterprises
Why insider threats go unnoticed: trusted access, fragmented signals, and weak controls hide risk until operations, data, and reputation are exposed.

How to Recover Compromised Accounts Fast
Learn how to recover compromised accounts with fast containment, evidence preservation, secure restoration, and controls that stop repeat access at scale.

How to Implement Zero Trust Without Slowing Operations
Learn how to implement zero trust with a phased plan that protects identities, data, devices, and operations while containing threats fast.

Digital Forensics After Cyber Attack Explained
Digital forensics after cyber attack preserves evidence, reveals attacker movement, and supports fast containment, recovery, and defensible reporting.

Identity Compromise Incident Response That Holds
Identity compromise incident response contains active account attacks, preserves evidence, and restores secure operations without widening disruption.

Network Segmentation for Ransomware Protection
Network segmentation for ransomware protection limits lateral movement, protects mission systems, and speeds containment when an attack begins.

Privileged Access Security Assessment That Holds
A privileged access security assessment exposes standing access, weak controls, and hidden pathways before attackers turn them into an operational incident

Enterprise Cyber Resilience Strategy That Holds
Build an enterprise cyber resilience strategy that limits blast radius, restores critical operations fast, and keeps leadership in control under attack.

Business Continuity After Cyber Attack: First 24 Hours
Business continuity after cyber attack depends on fast containment, clean recovery, and credible evidence that keeps operations moving under pressure today

How to Detect Malicious Insider Activity
Learn how to detect malicious insider activity with Zero Trust controls, behavioral signals, and response steps that protect critical systems much sooner.

How an Insider Threat Response Plan Holds the Line
Build an insider threat response plan that contains access abuse, preserves evidence, restores operations, and strengthens Zero Trust controls fast today.

How to Contain a Data Breach Before It Spreads
Learn how to contain a data breach with decisive isolation, evidence preservation, recovery, and Zero Trust controls that protect critical operations.

How to Improve Cloud Security for Business
Learn how to improve cloud security for business with Zero Trust controls, faster detection, and recovery plans that protect critical operations at scale.

Best Incident Response Services for Companies
Compare the best incident response services for companies and learn what separates rapid containment, recovery, and lasting cyber resilience in a crisis.

Managed Cybersecurity Services for Enterprise
Managed cybersecurity services for enterprise strengthen Zero Trust defenses, accelerate containment, and protect continuity when attacks disrupt business.

Enterprise Zero Trust Cybersecurity Solution
Choose an enterprise zero trust cybersecurity solution that verifies every request, limits blast radius, and keeps critical operations recoverable quickly.
Quantum Cryptography and the Next Security Perimeter
Quantum cryptography changes how enterprises protect critical data. Learn where it strengthens Zero Trust and where leaders must prepare now for risk ahead.

Compromised Account Recovery Services That Restore Control
Compromised account recovery services restore control, contain threats, and rebuild trust after attackers seize critical business access at full speed.

AI-Powered Next-Generation SIEM
See how an AI-powered next-generation SIEM improves detection, containment, and recovery while preserving analyst judgment and Zero Trust control daily.

Ransomware Recovery Services for Business
Ransomware recovery services for business restore operations fast, contain active threats, preserve evidence, and strengthen defenses after an attack.

Cyber Incident Response Retainer: Ready Before Impact
A cyber incident response retainer gives your organization immediate access to seasoned responders when containment, recovery, and continuity matter most.

Incident Response Services for High-Stakes Breaches
Incident response services that contain threats, restore critical access, and strengthen Zero Trust defenses when operations are under attack swiftly.

Zero Trust Security Architecture That Holds
Zero trust security architecture limits blast radius, protects critical assets, and keeps operations moving when identities, devices, or networks fail.